Anthropic reported on 22 October 2026 that, working with Theorem, it used Claude to patch bugs and produce formal proofs for 239 fuzz-test entry points across 123 open-source libraries. The company says the proofs cover compiled RISC-V binaries and total about 180 million lines of Rocq proof code. These are reported research results, rather than results independently reproduced for this article.[1]
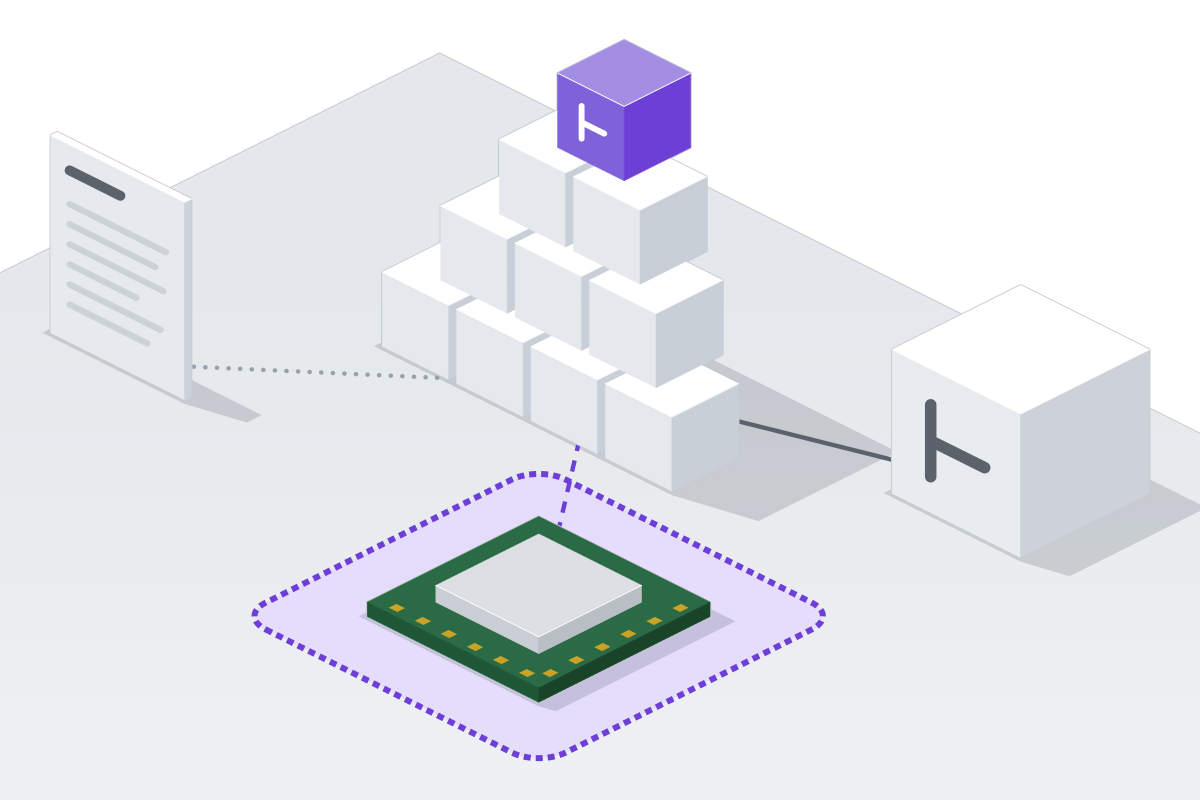
The workflow converts existing fuzz tests into mathematical specifications: the compiled test must exit normally without triggering specified crashes, including assertions and AddressSanitizer checks, for inputs smaller than 64 MB. Claude writes proofs that the Rocq kernel checks against those specifications. The modeled setting assumes a single-threaded, statically linked RISC-V binary, a fixed memory budget and Linux process semantics.[1]
Anthropic says it is publishing trusted components and complete proofs for fuzz tests that required no patches, alongside specifications it could not prove. It is withholding proofs that could expose unpatched bugs. Its stated trust base includes the exact theorem statements, the RISC-V and Linux formal models, and the Rocq checker.[1]
The limitations are substantial: the proofs concern binaries linked against musl libc, while deployments may use other architectures and dynamic linking. AddressSanitizer misses some memory-safety bugs; tested entry points do not cover an entire library, and callers can misuse it.[1]
[1]: Anthropic, “LLMs are making formal software verification feasible at a much larger scale,” 22 October 2026. https://www.anthropic.com/research/formal-verification
Sources
Check or correct this page
Verification record
The digest below shows whether the text you are reading matches the published source. It does not show that the reporting is correct. The build computes it from this page's Markdown source and lists it in the site manifest.
a212ac77c1a105e16a19606c5bda19ca49b2a8ba1dd4599998e944c8b8fd2d90