Researchers from the University of Maryland, Baltimore County, Hacker Factor and the US National Security Agency posted a security analysis of the Coalition for Content Provenance and Authenticity (C2PA) system to the Cryptology ePrint Archive on 23 April 2026.[1] The 11 authors examined version 2.2 of the C2PA specification, selected claim validators and version 0.1 of the conformance program. They say they performed the first formal-methods analysis of C2PA's core protocols.[1]
The authors report that the specification and conforming implementations achieve neither C2PA's claimed security goals nor further goals they consider essential.[1] Their formal analysis found that the tools that sign provenance claims and the validators that check them disagree on a signature's trusted timestamp, so timestamps can be altered.[1]
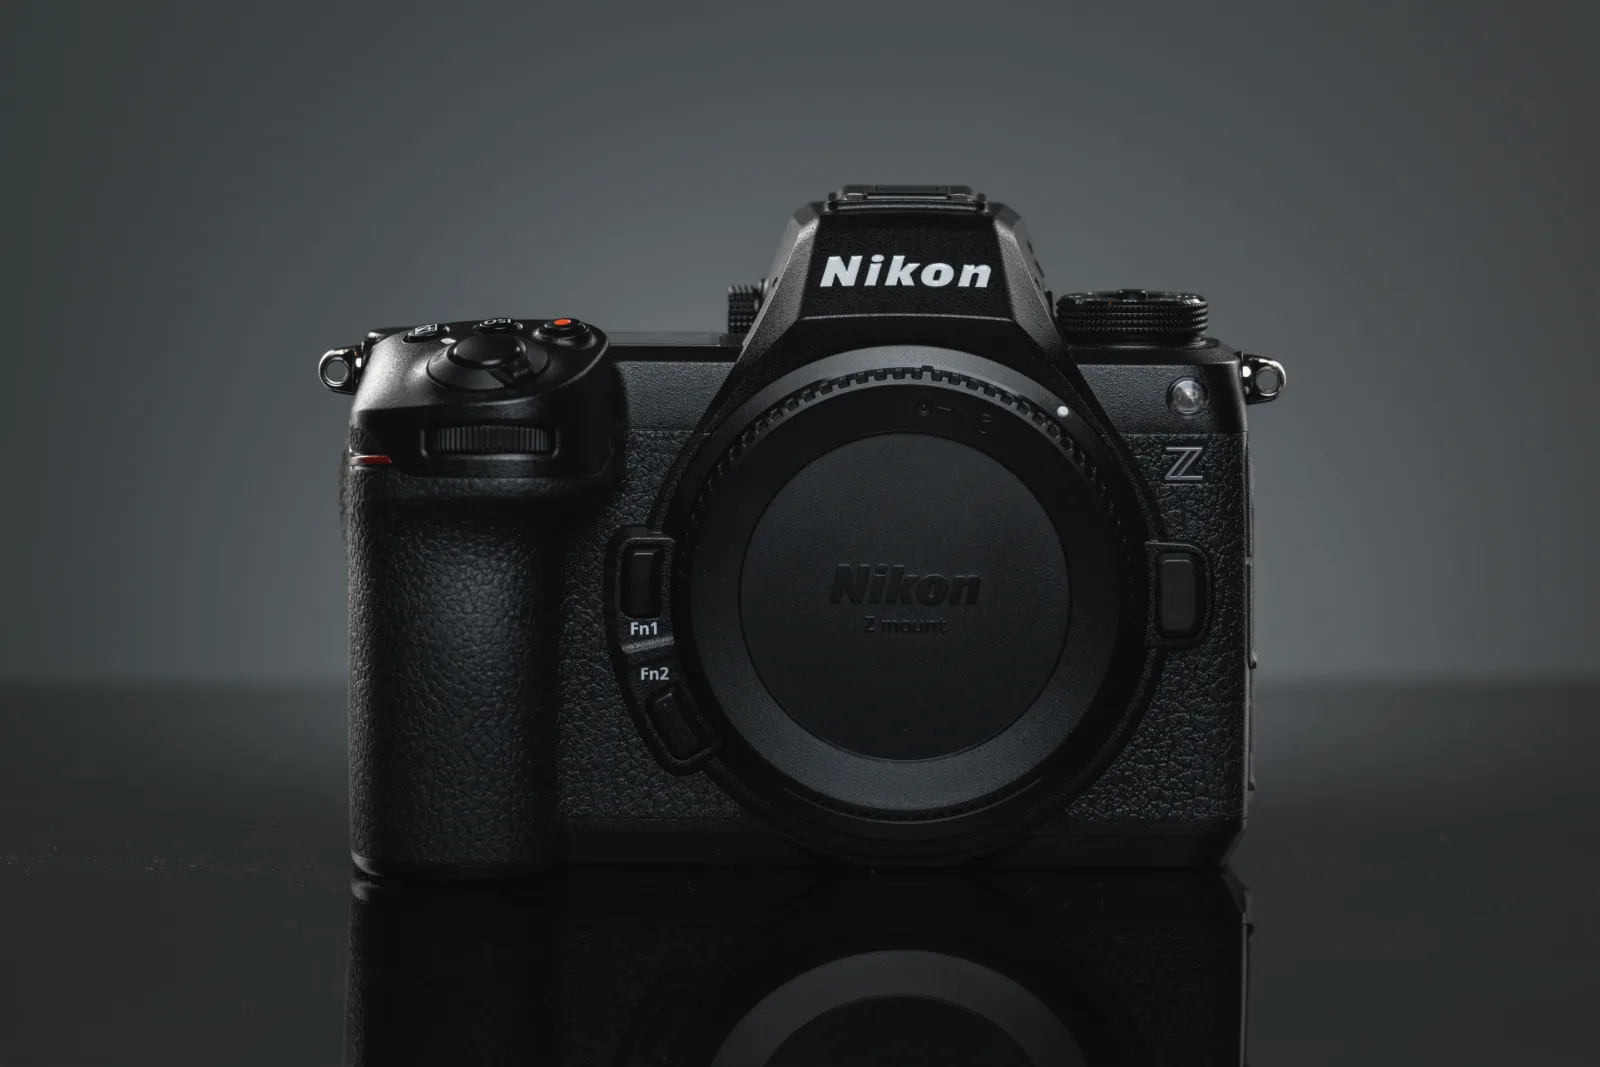
A companion arXiv summary posted on 27 April gives examples. After Nikon revoked a camera's signing certificate in November 2025, one conforming validator still reported a signature made with it as valid. Another reported it as invalid, and neither reported the revocation.[2] In another example, the authors changed the location data that a Pixel 10 Pro stores in an exclusion range, a part of the file the signature does not cover. A conforming validator did not detect the change.[2]
According to the authors, the conformance program certifies products largely on self-reported compliance, without examining a product's functionality or source code.[2] The C2PA launched the program in mid-2025.[4] It says the program helps ensure that any product displaying a Content Credential badge handles authenticity data accurately.[3]
The authors say the Pixel 10 Pro and version 2.3 of the specification adopted some of their proposed fixes, but version 2.4, from April 2026, does not address their concerns.[1, 2] They conclude that C2PA should not yet be relied on for high-stakes uses such as financial disclosures, journalism or legal evidence.[2]
Sources
Check or correct this page
Verification record
The digest below shows whether the text you are reading matches the published source. It does not show that the reporting is correct. The build computes it from this page's Markdown source and lists it in the site manifest.
1a756eb31bb31169e9de5c388568bc356b03e216211d172bd50e360c8d959686